Anthropic · Status at source date: Newsletter archive
Anthropic discloses a US export-control directive affecting Fable 5 and Mythos 5
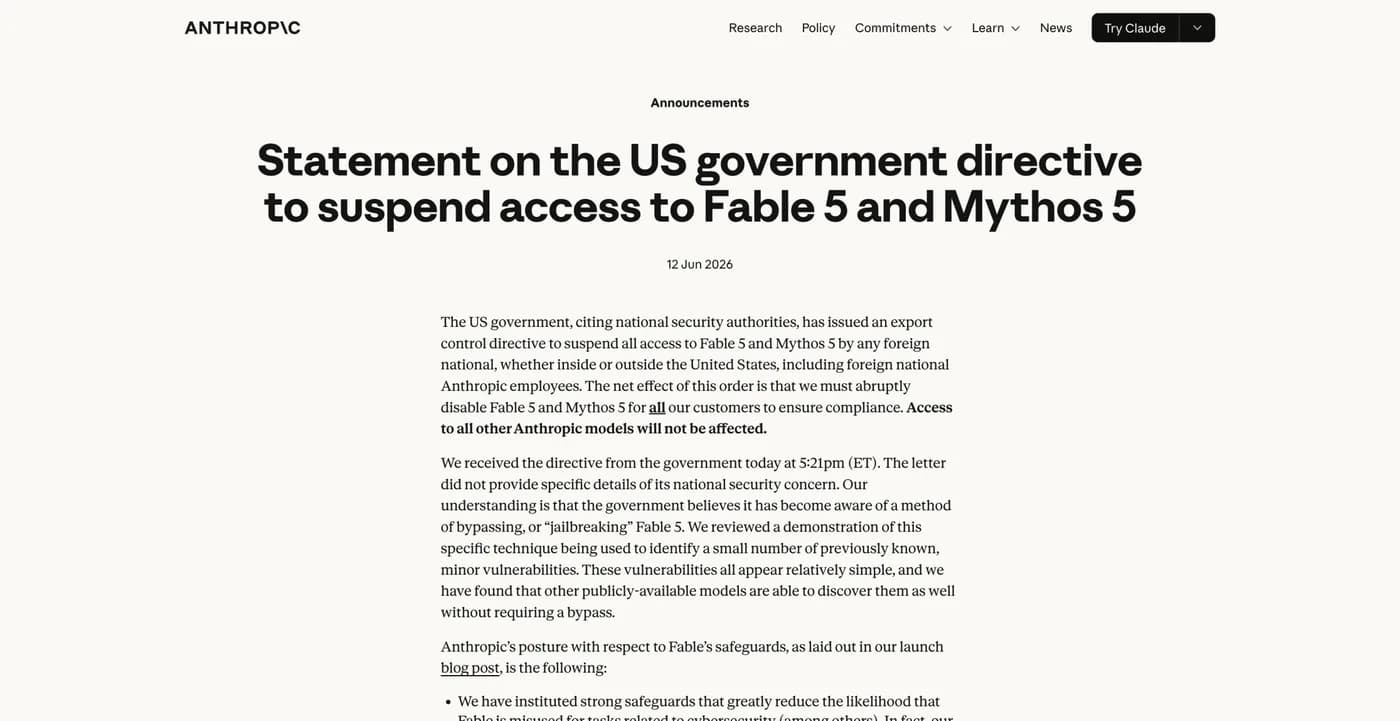
Anthropic has disclosed a US government export-control directive, citing national-security authorities, that suspends access to its Fable 5 and Mythos 5 models for any foreign national, whether inside or outside the United States, including foreign-national Anthropic employees. To comply, Anthropic said it had to abruptly disable both models for all customers as of the evening of 12 June; access to all other Anthropic models remains unaffected.
What changed
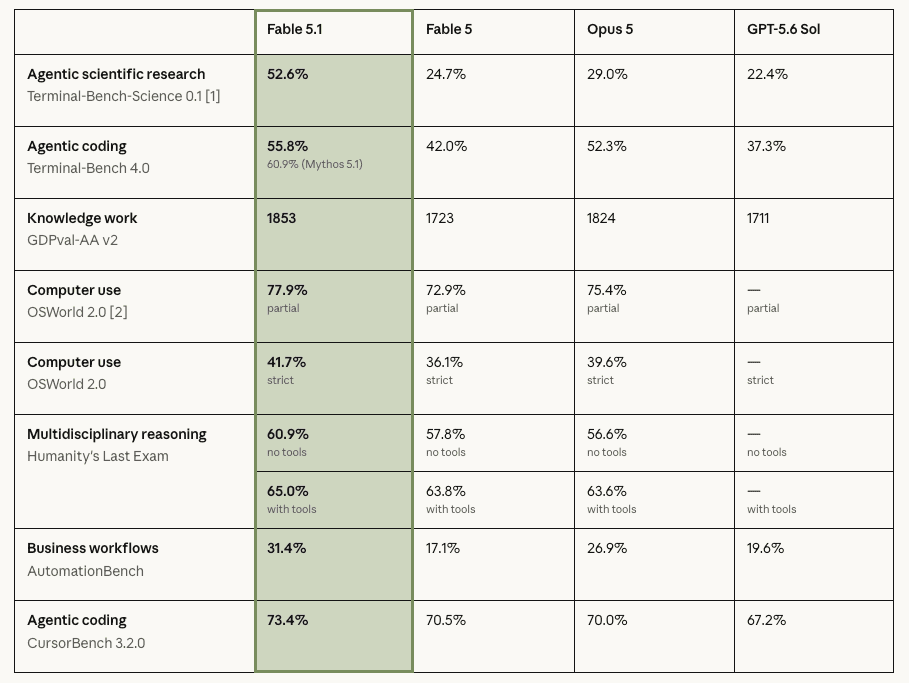
In its statement, Anthropic said the directive did not specify the national-security concern, but that its understanding is the government believes it has found a method of "jailbreaking" Fable 5. Anthropic reviewed a demonstration and said the technique surfaced a small number of previously known, minor vulnerabilities that other publicly available models, including OpenAI's GPT-5.5, can also find without a bypass. The company said no universal jailbreak has been found, that it had red-teamed Fable's safeguards for thousands of hours with the US government, the UK AISI, and third parties before launch, and that it adopted a "defence in depth" strategy backed by 30-day data retention to detect and shut down attacks.
Anthropic said it is complying with the legal directive while disagreeing that a narrow potential jailbreak should justify recalling a commercial model used by hundreds of millions, arguing the same standard would halt new model deployments across the industry. It called the action a likely misunderstanding and said it is working to restore access, while reiterating its view that governments should be able to block unsafe deployments through a transparent, fact-based statutory process.
Why it matters for advertisers
For you, this means teams relying on these specific frontier models should expect disruption and have a fallback plan, while most Anthropic usage remains unaffected. Worth confirming which models your workflows depend on, so a sudden access change does not stall delivery.
Perspective from the original PMC newsletter.Sources & contributor credit
- Newsletter coverage · Paid Media Collective newsletter
Original newsletter text, contributor labels and media for this update.
- Source referenced in newsletterAnthropic
Linked from the original newsletter. The source publication date has not been independently confirmed.

Original creator unverified
The original creator has not yet been verified. Newsletter curation and publication do not establish original authorship.
Attribution evidence and limitations
Full attribution review pending.
A source link alone does not establish original authorship.
Original image and video creators have not yet been verified.
- Published on this site
This update reflects the dated source reporting. Availability may have changed. Further coverage of this same development will be added to this page.
Original newsletter text and archive evidence
Anthropic discloses a US export-control directive affecting Fable 5 and Mythos 5
Anthropic has disclosed a US government export-control directive, citing national-security authorities, that suspends access to its Fable 5 and Mythos 5 models for any foreign national, whether inside or outside the United States, including foreign-national Anthropic employees. To comply, Anthropic said it had to abruptly disable both models for all customers as of the evening of 12 June; access to all other Anthropic models remains unaffected.
In its statement, Anthropic said the directive did not specify the national-security concern, but that its understanding is the government believes it has found a method of "jailbreaking" Fable 5. Anthropic reviewed a demonstration and said the technique surfaced a small number of previously known, minor vulnerabilities that other publicly available models, including OpenAI's GPT-5.5, can also find without a bypass. The company said no universal jailbreak has been found, that it had red-teamed Fable's safeguards for thousands of hours with the US government, the UK AISI, and third parties before launch, and that it adopted a "defence in depth" strategy backed by 30-day data retention to detect and shut down attacks.
Anthropic said it is complying with the legal directive while disagreeing that a narrow potential jailbreak should justify recalling a commercial model used by hundreds of millions, arguing the same standard would halt new model deployments across the industry. It called the action a likely misunderstanding and said it is working to restore access, while reiterating its view that governments should be able to block unsafe deployments through a transparent, fact-based statutory process.
For you, this means teams relying on these specific frontier models should expect disruption and have a fallback plan, while most Anthropic usage remains unaffected. Worth confirming which models your workflows depend on, so a sudden access change does not stall delivery.
Source captured . No explicit first-contributor label was provided for this update.